
How to Spot a Crypto Scam: Key Warning Signs
Crypto scams are usually exposed by promises of guaranteed returns, demands to act immediately, requests to transfer coins or disclose sensitive information, and the inability to independently verify the organizers. The more of these signs appear together, the higher the risk. Before transferring funds, separately verify the website address, team, contract, withdrawal terms, and project reputation.
The general verification principle is simple: separate the seller’s claims from facts you can confirm without their help. A polished website, thousands of followers, office photos, chat testimonials, and the logo of a well-known company prove nothing on their own. All these elements can be copied, purchased, or created within hours. Only verifiable information matters: a legal entity listed in an official registry, domain history, a public team with a verifiable track record, open-source code, a smart contract audit, and actual on-chain transactions.
What Red Flags Point to Crypto Fraud
The most serious red flags are guaranteed returns, a secret strategy, a bonus available only for an urgent transfer, communication exclusively through a messaging app, and a requirement to top up your balance before making a withdrawal. A legitimate service explains the risks, fees, and account recovery process in advance. A scammer conceals details, changes the terms after payment, and prevents you from consulting an independent expert.
A single sign does not always indicate fraud. A young legitimate project may lack a long track record, while a decentralized service may have no registered company. However, the absence of a legal entity combined with an anonymous team, closed-source code, unrealistic returns, and aggressive sales tactics already forms a consistent pattern of risk. If there are two serious red flags, it is reasonable to stop the transfer; if you are asked to disclose your seed phrase, end the conversation immediately.
How to Quickly Verify a Cryptocurrency Offer
A quick check consists of five independent steps: find the official source, verify the domain, investigate the recipient, check the contract, and test withdrawals with a minimal amount. Search for the information yourself rather than opening links sent by the other party. If even one critical point cannot be verified, the safe decision is not to transfer funds until you receive confirmation.
- Enter the company name manually and find its website through several independent sources. Compare the domain spelling and its registration date.
- Check the team members’ names, older profiles, previous projects, and mentions outside promotional publications.
- Review the wallet address in a blockchain explorer: its age, number of transactions, sources of incoming funds, and bulk transfers to exchanges.
- For a token, examine the contract, supply distribution, owner privileges, coin concentration, and whether the token can be sold.
- Do not send the full amount as a test. Even a successful small withdrawal does not prove legitimacy: pyramid schemes deliberately allow initial payouts.
Customer Support Does Not Need Your Seed Phrase
Twelve or twenty-four words provide full control over a wallet. Never enter them on a website reached through a link, send them to an employee, dictate them over the phone, or reveal them while sharing your screen. Legitimate support may ask for a public address or transaction hash, but never for your recovery secret.
The HTTPS padlock is not proof of trustworthiness either: it only encrypts the connection to the selected website, even if that website belongs to a criminal. Check the exact domain name and the contents of the wallet request. Approve or permit permissions with an unlimited amount are particularly dangerous: once signed, they may allow an attacker to transfer assets later without requesting confirmation again.
The Most Common Types of Crypto Scams
Users most often encounter phishing, fake support, investment pyramid schemes, rug pulls, honeypot tokens, fake giveaways, romance scams, and malicious apps. These types differ in how victims are contacted and in their technical implementation, but they pursue one of two goals: inducing the victim to transfer cryptocurrency voluntarily or gaining access to their wallet.
Phishing imitates the website of an exchange, wallet, airdrop, or DeFi service. The user follows an advertisement, message, or lookalike domain, then enters a seed phrase or signs a malicious permission. One specific variation is address poisoning: the scammer creates an address with similar first and last characters and sends a small transaction, hoping the owner will later copy the recipient from their transaction history.
Fake support agents seek out people who have publicly complained about a pending transfer or wallet error. The “specialist” offers synchronization, verification, or fund recovery, then sends a phishing form. Legitimate support staff do not initiate private conversations without a support request and never ask for secret keys. A ticket number, public address, and transaction ID are sufficient.
| Scheme | Main Lure | What the Scammer Demands | Telltale Sign |
|---|---|---|---|
| Phishing | Login, airdrop, wallet verification | Seed phrase or signature | Lookalike domain and pressure to act urgently |
| Pyramid scheme | Consistently high returns | A deposit and recruitment of new participants | Payouts depend on new deposits |
| Rug pull | Rapid growth of a new token | Purchase via a DEX | Liquidity controlled by the team |
| Honeypot | Token with a rising price | Token purchase | You can buy but cannot sell |
| Fake giveaway | Doubling the coins sent | Upfront transfer | The gift requires payment first |
| Romance scam | Relationship and shared plans | Deposit on the specified platform | Trust is built over several weeks |
| Malicious app | Wallet or trading service | Installation and granting permissions | Unofficial file or publisher |
How a pyramid scheme differs from a rug pull and a honeypot
A pyramid scheme pays earlier participants with money from new ones, a rug pull ends with the creators withdrawing liquidity or selling off tokens, while a honeypot technically blocks regular buyers from selling. On the surface, all three schemes may show a growing balance, an active community, and early payouts, so you need to verify the source of returns and the contract code.
A crypto investment pyramid often masquerades as an arbitrage bot, mining, copy trading, or asset management service. The account dashboard displays returns that are not confirmed on the blockchain. The first small withdrawals may actually go through, building trust and encouraging a larger deposit. When the victim requests a large withdrawal, a “tax,” “insurance fee,” “AML fee,” or mandatory top-up appears.
In a rug pull, the developer retains the ability to withdraw liquidity, mint additional tokens, change fees, or block addresses. After promoting the token and driving up its price, the team exercises these powers, leaving buyers with a worthless asset. Locked liquidity reduces one risk but does not guarantee safety: the contract may contain other administrative functions, while a large share of the supply may be held in connected wallets.
A honeypot appears liquid because purchases go through and the price rises. However, the contract may prohibit everyone except trusted addresses from selling, impose a nearly 100% fee, or change the rules after purchase. A transaction simulator and source code analysis can help detect these restrictions, but they offer no absolute guarantee if the owner can change the parameters later.
How fake giveaways and romance crypto scams work
A fake giveaway promises to return twice as many coins after a verification transfer, while a romance scam first establishes an emotional connection and only then proposes an investment. In both cases, the transfer is irreversible, and the displayed balance does not prove ownership of the assets. A legitimate giveaway does not require you to send cryptocurrency in advance to receive a prize.
Fake giveaways use hacked accounts, fake livestreams, images of well-known entrepreneurs, and pages that mimic official projects. A timer, participant counter, and list of supposedly completed payouts create the illusion of high demand. Sometimes an NFT or airdrop is promised, but instead of requesting a transfer, the site asks you to connect your wallet and sign a token spending approval.
A romance scam develops more slowly. Someone met through an app or social network communicates regularly, talks about their own success, and introduces the victim to a “trusted” exchange. They first suggest a small deposit, then display profits on a fake platform and allow a test withdrawal. After a large deposit, access is blocked. Requests to pay for medical treatment, tickets, or customs duties may also end with funds being sent to an address controlled by criminals.
The dangers of fake crypto apps
Fake crypto apps steal seed phrases, replace recipient addresses, read the clipboard, or display a fictitious trading balance. The threat may come not only from an installer received in a message, but also from an app that temporarily made it into an official store. You should verify the developer, official domain, update history, permissions, and file checksum.
Installing a wallet safely
Open the project's official website manually, follow its link to the app store, and verify the publisher's name. Do not install an APK, EXE, or extension received in a private message. For significant amounts, use a separate device or hardware wallet, and test any new software with an empty test wallet first.
How scammers persuade people to send cryptocurrency or give up access to their wallets
Scammers secure transfers or access by combining urgency, authority, the promise of profit, and fear of loss. They do not necessarily rely on a single request: more often, they gradually draw the victim in, persuade them to take a small, seemingly safe action, demonstrate fabricated success, and only then demand a large transfer, seed phrase, or malicious signature.
Social engineering works not through sophisticated technology but by controlling attention. The scammer adopts a credible role—an exchange employee, analyst, developer, government official, or acquaintance—while limiting the time available for verification. While the victim is focused on saving an account, avoiding missed profits, or helping someone close to them, they are less likely to notice inconsistencies in the domain, documents, and payment process.
How urgency, authority, greed, and fear influence decisions
Urgency leaves no time, authority reduces the desire to question, greed shifts attention to future profits, and fear drives people to prevent imagined harm. These tactics are particularly effective in combination: for example, a “security employee” reports a breach and demands that assets be transferred immediately to a supposedly secure address.
| Pressure tactic | Typical phrase | Scammer's goal | Safe response |
|---|---|---|---|
| Urgency | “Your account will be blocked in 15 minutes” | Prevent you from verifying the information | End the conversation and log in through the official website |
| Authority | “I'm from the exchange's security team” | Elicit automatic compliance | Open a support ticket yourself |
| Greed | “This return is only available today” | Pressure you into increasing the transfer amount | Verify the source of the returns and the risk of loss |
| Fear | “Someone is already trying to withdraw your coins” | Trigger a panic-driven action | Do not follow the link; check your transaction history |
Scammers often fake authority using technical details. The caller may mention part of your address, your name, phone number, or a recent transaction—information that may be public or obtained from a data breach. Knowing these details does not prove that the person represents the exchange. Their identity can only be verified through an official channel that you access independently of the incoming message.
Greed is not limited to promises of spectacular profits. A subtler lure might be a plausible 8–15% annual return, access to a private sale, or a discount on a well-known asset. The figures may seem modest, but the mechanism remains fraudulent: money is sent to an unknown person, the obligations cannot be verified, and withdrawals depend on further payments.
How victims are drawn in gradually
Gradual involvement begins with harmless contact, continues with a small request, and ends in financial dependence. Each completed step builds trust and makes it harder to walk away: after weeks of communication, an initial deposit, or a fee already paid, it is psychologically difficult to admit that something is wrong. This is why the point at which you stop should be determined by rules, not emotions.
- The scammer makes contact through an ad, an unsolicited message, a support chat, a dating site, or a comment about a wallet issue.
- They gather information about the victim's income, experience, exchanges, and available assets while demonstrating expertise and personal attention.
- The victim is offered a low-risk action: signing up, installing an app, connecting an empty wallet, or depositing a small amount.
- The fake dashboard shows a profit, and a small withdrawal may even be paid out using money from other victims.
- Once trust has been established, the scammer persuades the victim to deposit the main amount, take out a loan, or involve relatives.
- When the victim tries to withdraw funds, they are asked to pay a tax, fee, deposit, or liquidity verification charge, or complete another “verification” by making a transfer.
An additional payment will not unlock stolen funds
If an unknown platform asks you to send cryptocurrency to pay a tax, complete an AML check, activate withdrawals, or prove ownership of a wallet, another payment will usually only increase your loss. Legitimate fees are either disclosed in advance or deducted from the amount being withdrawn. Tax authorities do not collect payments by asking you to transfer funds to a manager's personal crypto address.
Another tactic is isolation. The scammer asks you not to discuss the transaction with your bank, exchange, or relatives, citing confidentiality, the risk of being blocked, or the secrecy of the strategy. This request protects the scam, not the client. Taking an independent pause is more valuable than any promised bonus: close the chat, save the conversation, and verify the claims through official contacts.
What to do if you are being rushed into signing a transaction
If you are being rushed into signing a transaction, reject the request and determine what permissions it grants, to which contract, and for what amount. A signature may require no gas fee but still have dangerous consequences: permit, Permit2, and other messages can authorize tokens to be transferred later without further confirmation from the user.
A safe rule: no support agent, investor, or new acquaintance should dictate the address to which you transfer all your assets or ever see your seed phrase. Any claim that your wallet urgently needs to be secured should be verified from another device and through an official channel you found independently.
If you have already taken the action, speed matters, but panic is harmful. Disconnect the wallet from the suspicious site, revoke dangerous approvals through a trusted service, transfer the remaining assets to a new wallet with a new seed phrase, and alert the exchange if the funds were sent to one of its addresses. A recovery secret entered on someone else's page even once must be considered fully compromised: changing the password will not resolve the problem.
How to evaluate a crypto project and its team before investing
A crypto project should be evaluated through a chain of independent checks: examine the age and ownership of its website, compare its documents with the actual product, and verify the team's experience, legal details, partnerships, funding sources, and development history. Neither an attractive website, well-known advisers, nor an audit alone proves reliability—the consistency of all the facts is what matters.
How to check a crypto project's website and documents
Start with the domain: check its registration date, the website's change history, and archived versions of its pages. A domain created a few weeks ago does not necessarily belong to scammers, but it should not be presented as a project with a long history. Warning signs include an undisclosed name change, copied content, broken links, generic employee profiles, and no earlier versions of the website.
The white paper, tokenomics, roadmap, and user agreement should be read together. Check whether they describe the token's purpose, total supply, coin allocation, unlock schedule, holder rights, and ways of generating returns consistently. If the home page promises fixed profits while the documents describe the token solely as an in-game or utility token, this is a significant contradiction.
Do not treat a lengthy white paper as proof of quality. Look for specific information: what problem the product solves, why it requires blockchain, who will pay to use it, whether any code exists, and where the revenue comes from. Generic statements about artificial intelligence, decentralization, and a “revolutionary ecosystem” without details on architecture, metrics, and limitations do not allow the proposed model to be verified.
How to Verify a Crypto Project's Team
Do not merely check for photos and biographies; verify the professional history of each key team member. Look for older profiles, talks, publications, previous employers, and projects that existed before the token launch. Link each person to the project through an independent source, such as a personal page, employer profile, conference recording, or repository with a long history.
It is worth running reverse image searches on the founders' photos: they may belong to other people or may have been generated. A recently created profile with hundreds of connections, identical recommendations, and no older activity is less credible than one showing years of discussions and real colleagues. An anonymous team carries greater risk, as your assessment will have to rely solely on the code, the management of funds, and whether those responsible can be held accountable.
A Well-Known Name Is No Substitute for Verification
Scammers add people to the Team section without their consent or describe public experts as “advisors.” Check whether the individual mentions the project on their own verified profile. A screenshot of a conversation, a conference photo, or a company logo on the project's website does not prove a partnership.
How to Verify Legal Claims and Partnerships
Record the legal entity's full name, registration number, country, address, and directors' names. Then find the company in the official government registry and compare its dates, status, and business activities. The registration of a legal entity only proves that it exists; it does not confirm that it is licensed to hold funds, manage investments, exchange cryptocurrency, or accept deposits.
Verify a license in the stated regulator's registry using its number and the company name, not an image of the certificate. Check exactly who it was issued to, which services it authorizes, and whether it is currently valid. Scammers use license numbers belonging to similarly named organizations, permits issued to another company in the group, or an ordinary service provider registration, presenting them as a government guarantee for investments.
A partnership should be confirmed by the other party. Look for a press release, integration page, documentation entry, or public statement by the partner's representative. Phrases such as “working with,” “supported by,” and “using the technology of” may simply mean that the project purchases a standard cloud service. Verify a fund's investment on the fund's own website and in its portfolio, not only in the project's publications.
| Project Claim | Strong Evidence | Weak Evidence | Red Flag |
|---|---|---|---|
| Licensed | Entry in the regulator's registry specifying the authorized services | Scanned certificate on the website | The number belongs to another organization |
| Has a partner | Confirmation on the partner's official website | A photo together or a logo | The partner publicly denies any connection |
| Fund investment | The project is listed in the fund's portfolio | A republished project press release | The fund or its employees do not exist |
| Working product | An accessible version, code, and verifiable operations | A recorded demo | Access is repeatedly promised only after the token sale |
How to Evaluate a Project's Product, Community, and Track Record
Test the product with a small transaction without connecting your main wallet. Check whether you can perform the claimed action, view the transaction in a block explorer, and withdraw assets. Evaluate the repository based on meaningful changes, the number of independent developers, open issues, and releases. Hundreds of minor automated commits or copied code create the appearance of activity but do not prove that development is taking place.
When assessing the community, focus on the quality of discussions rather than the number of followers. Repetitive praise, bans on questions about withdrawals, the immediate deletion of criticism, and administrators who initiate private conversations are typical of high-risk schemes. Ask a specific question about the budget, token unlocks, or a delayed release and assess whether the team responds with facts.
Reconstruct the timeline: website launch, funding rounds, contract deployment, audits, releases, tokenomics changes, and previous names. Compare the roadmap's promised dates with the actual results. A single delay is normal in development; repeatedly changing goals, deleting old promises, and raising more money without delivering a finished product indicate increased risk.
The Independent Verification Rule
For every important claim, find at least two sources that the project does not control. Even after verification, do not transfer the entire amount at once: use a separate wallet, start with a small transaction, and test withdrawals in advance. If a key fact cannot be confirmed, treat it as unverified rather than “probably true.”
How to Check a Token for Scams, Honeypots, and Rug Pulls
To check a token, find the exact contract address in official sources, examine its code and owner privileges, and check its liquidity, token distribution, taxes, supply, and actual sales. Then make a minimal purchase and sale using a separate wallet. An automated scanner is useful as a filter, but it does not guarantee safety or replace transaction analysis.
How to Find the Correct Token Contract
Look for the contract address on the official website, in the documentation, and in the project’s verified profile, then make sure all sources list the same address. A name and ticker can be copied in minutes, so searching for a token by symbol alone is dangerous. In the blockchain explorer, check the creation date, creator, source code verification, number of holders, and links to the official project.
Unverified code cannot be fully matched against the deployed bytecode, increasing the risk. A verified contract is not a mark of quality either: malicious logic may be publicly visible. If a proxy contract is used, find the implementation address and upgrade administrator. The ability to replace the implementation makes it possible to change the rules after purchase, even if the initial version appeared safe.
How to Check Owner Privileges and Token Supply
Examine the functions available to the owner, administrator, or special roles. Administrative rights are not inherently dangerous; the risks lie in their scope, lack of transparency, and absence of restrictions. The contract may allow new tokens to be minted, addresses to be frozen, transfers to be paused, fees to be changed, selected wallets to be exempted from taxes or restrictions, and the swap router to be replaced.
The label “ownership renounced” does not guarantee safety. Privileges may remain with another role, an external contract, or a proxy administrator; malicious parameters may have been set before ownership was renounced. Check role assignment events and the current addresses of administrative accounts. A multisig and execution delay reduce risk only when the participants are independent and the delay cannot be bypassed.
| Parameter | Safer Model | Higher Risk | What to Check On-Chain |
|---|---|---|---|
| Supply | Fixed or subject to rule-based issuance limits | Unlimited minting controlled by one address | Minter roles and minting events |
| Fee | A public cap that cannot be raised sharply | The owner can set it to 100% | Functions for changing the buy tax and sell tax |
| Restrictions | Limited and transparent conditions | Arbitrary blacklist or selling restriction | Roles and exemption lists |
| Upgrades | Delay and multisig | Instant upgrade with a single key | Proxy administrator and timelock |
How to Check a Token for Honeypot Restrictions and Sellability
A honeypot allows users to buy a token but prevents ordinary users from selling it. This may be caused by a direct restriction, blacklist, hidden fee, maximum transaction limit, or a condition that allows only selected addresses to sell. A simulator detects many variants, but its results depend on the contract’s current state: the owner can change the settings after the check.
The most practical check is to buy the minimum amount and immediately sell part of it through the same pool. Use a new wallet with no valuable assets, manually verify the token address, and decide in advance how much you are willing to lose to fees and slippage. A successful sale confirms only that an exit is currently possible; it does not rule out a future freeze, liquidity removal, or tax increase.
Compare the estimated amount with the amount actually received. A fee of a few percent may be part of the tokenomics, but taxes of 20–30% make exiting much harder, while the owner’s ability to raise them to 100% is effectively equivalent to blocking sales. Do not increase slippage without understanding why: advice to set it to 49% or 99% often conceals an excessive tax or price manipulation.
A Successful Simulation Does Not Guarantee a Sale
A scam contract may recognize the addresses of popular scanners, temporarily disable restrictions, or allow small sales while blocking large ones. Check an actual transaction, the sales history of different wallets, and the administrator’s privileges. Do not connect your main wallet to an unknown verification site or sign unclear approvals.
How to Check Token Liquidity and Rug Pull Risk
Find the main trading pool and assess not only the dollar value of its liquidity but also who owns the LP tokens or concentrated liquidity position. If the team controls almost all the liquidity and can withdraw it immediately, the price could collapse in a single transaction. A lock should be verified through the contract of a reputable service, including the address, duration, and percentage of the position locked.
Check the lock duration and unlock conditions. Locking 95% of the liquidity for a year is substantially different from locking 20% for seven days. Burned LP tokens cannot be recovered through ordinary means, but this does not protect against additional issuance, the sale of team reserves, the creation of another pool, or a contract vulnerability. Concentrated liquidity may be represented by an NFT position, so older scanners sometimes display it incorrectly.
How to Check Token Distribution and Holder Wallets
Open the list of top holders and exclude the liquidity pool, burn address, bridge, and verified vesting contracts from your analysis. Then group regular wallets by funding sources, transfers between them, and when they received the tokens. Ten addresses holding 4% each may belong to the same person, so each wallet’s nominal share can conceal the actual concentration.
Large unlocked reserves, simultaneous transfers to an exchange, multiple wallets funded by a single address, and sales immediately after a promotional campaign are particularly dangerous. Compare the on-chain distribution with the tokenomics: the team, marketing, and early investor allocations should match, and vesting should be enforced by a contract. A spreadsheet with a promised schedule is less reliable than a public lockup contract.
Review the creator’s early transactions: which contracts they deployed, where they withdrew funds, and whether they are linked to tokens that have already collapsed. Reusing wallets makes verification easier, but a lack of history proves nothing—a scammer can create new addresses. The final assessment should consider the code, governance, liquidity, concentration, and behavior of related wallets together.
How to Tell a Genuine Website, Wallet, or Exchange from a Fake
A genuine website, wallet, or exchange is identified by its exact domain and installation source, not by its logo or appearance. Obtain the address from a previously saved bookmark, official documentation, or a verified company profile, then check the spelling, connection, and app publisher. Any request to enter a seed phrase indicates a fake or a dangerous scenario.
How to Verify a Crypto Service Domain
Read the address from right to left: first identify the top-level domain and primary domain name, then the subdomains. In wallet.example.com, wallet belongs to the owner of example.com, while in example.wallet-login.com, the primary domain is wallet-login.com. Scammers replace letters with similar-looking characters, add hyphens or words such as secure and support, use a different top-level domain, or place a well-known name in a subdomain.
Check the domain’s registration date and history, especially if the service claims to have operated for many years. A new domain may be official for a separate product, but it should be linked from the established website or an official account. Expand shortened links before opening them, without connecting your wallet. A QR code also contains a regular address and is not inherently safe simply because of its format.
Do HTTPS and a Certificate Protect Against Phishing?
HTTPS encrypts the connection to the domain you opened, but it does not confirm that its owner is trustworthy. A phishing site can obtain a valid certificate and display a secure connection icon. A certificate helps identify basic errors and traffic interception, but the exact domain name remains the key consideration; never bypass a browser certificate warning.
Open the connection details and make sure the certificate was issued for the current domain and is valid, but do not expect it to prove that the brand is official. Most modern certificates verify control of a domain, not the identity of the business. HTTPS is a minimum technical requirement; its absence on a login page is sufficient reason to close the page immediately.
| Indicator | Official Service | Phishing Copy | Reliable Check |
|---|---|---|---|
| Domain | Matches the documentation and established links | Look-alike spelling, a hyphen, or a different top-level domain | Compare the address character by character |
| App | Linked from the official website, with a matching publisher | A clone with a similar name and manipulated reviews | Check the publisher, history, and developer link |
| Login | Uses a password, device key, or wallet connection | Requests a seed phrase for “synchronization” | Never enter your seed phrase anywhere |
| Transaction | The parameters match the selected action | Requests an unlimited approve or an unclear signature | Verify the address, network, amount, and permissions |
How to safely install a wallet or exchange app
Open the app store using a link from the official website, not by searching for the app name. Check the developer, the number and history of updates, the publication date, the privacy policy, and the publisher’s website address. A high store ranking and positive reviews do not rule out a fake: reviews can be bought, and a malicious update may appear after a period of normal operation.
For desktop software, check the official repository or download page, as well as the digital signature and checksum if the developer publishes them. Do not install APK files, archives, or “security updates” sent by a support representative via messenger. Legitimate support will not ask you to install remote access software, disclose your seed phrase, or transfer assets to a “safe” address.
Your seed phrase is not required for verification or support
A seed phrase can fully restore a wallet and provides control over its assets. Enter it only when you intentionally restore a wallet in a trusted app. An exchange website, support form, bot, extension, or “synchronization specialist” should never request it. If the phrase has already been exposed, create a new wallet and transfer the assets as quickly as possible.
Can you trust crypto service ads in search results?
You should not trust a sponsored link simply because the search engine labels it as an ad or places it above the official result. Scammers buy ads targeting the name of an exchange or wallet, copy the headline, and direct users to a lookalike domain. Do not use an ad to sign in: manually enter the address you previously saved or use a bookmark.
Even an organic search result may lead to a fake website due to search manipulation, a compromised third-party page, or a malicious extension. After your first verified visit, bookmark the page. If the service unexpectedly displays a different sign-in form, asks you to restore your wallet, or warns of an urgent account suspension, stop and verify the address again through an independent channel.
How to verify a browser extension and website interface
Install extensions using links from the official documentation and verify the publisher. A very low installation count, a recent publication date, errors in the description, or a request to access every webpage without a clear reason warrant additional checks. Review your list of extensions periodically: remove unknown ones and disable those you do not use, especially extensions that can read and modify website data.
A phishing interface is often almost visually indistinguishable from the genuine one, so do not look only for errors in the text. Compare section URLs, menu behavior, the help center, notification history, and sign-in methods with a previously saved version. Warning signs include mandatory seed phrase import, a sudden demand to remove all limits, signing a blank message, or permission to spend an unlimited number of tokens.
Before confirming, check the details in the wallet window rather than the explanation on the website: the network, contract address, amount, recipient, and permission type. A hardware wallet protects the key from extraction but cannot prevent you from signing a malicious transaction. Use a separate wallet with a small balance for new services, and revoke unnecessary permissions after the transaction.
A safe way to access a crypto service
Find the domain through several official sources, verify it once, and bookmark it. Install apps and extensions only through links on that domain. Check the address before signing in and the details in your wallet before signing. This process offers better protection than trying to identify a fake by its design.
How to identify a scammer on Telegram, Discord, social media, or support channels
Warning signs include an unsolicited direct message, urgency, a request to disclose your seed phrase or connect your wallet, and discrepancies between the account’s name, username, history, and official information. Legitimate administrators generally do not initiate conversations, require a transfer for “verification,” or offer to resolve an issue through a private link.
How to tell a fake administrator from a real one
Check the unique username, numeric ID, server roles, and how the conversation began rather than the avatar and display name. A scammer can copy an employee’s photo, bio, and name but cannot use the same username. The difference may be a single character: a lowercase l instead of an uppercase I, the digit 0 instead of the letter O, an extra underscore, or a character from another alphabet.
Open the project’s official website using a saved bookmark or an address from an independent directory, find its community links, and follow them again. Then find the administrator in the member or role list and compare their profile with the person contacting you. Do not trust a link to an “official chat” sent by a stranger, as it may lead to a fully cloned community.
| Indicator | Legitimate support | Fake representative | What to check |
|---|---|---|---|
| Initial contact | Responds to a ticket created by the user | Sends the first direct message | Whether a request exists in the official ticketing system |
| Wallet access | Requests a public address or transaction hash | Requests a seed phrase, key, or screen access | Whether the issue can be resolved without sensitive information |
| Link | Leads to a domain listed in the official documentation | Uses a lookalike domain or URL shortener | The full domain name before opening the link |
| Payment | Does not require a deposit to process the request | Requests a fee, security deposit, or test transfer | Whether such a payment is listed in the service rules |
Dangerous Direct Messages and Verification Methods
Any message asking you to enter your seed phrase or private key, or sign an unclear permission to claim an airdrop, restore access, sync a wallet, or verify ownership is dangerous. You can share your public address and transaction hash with support, but administrators, developers, and security teams never need your secret words.
Fake verification is often disguised as a CAPTCHA, Collab.Land prompt, support form, or “Are you human?” check. Clicking it opens a cloned website that asks you to connect your wallet and sign a message. A simple signature may be safe only if the text is clear and the domain is known; a transaction involving approve, permit, setApprovalForAll, or an asset transfer changes permissions and may grant access to your tokens.
Support Cannot Restore a Wallet Using a Seed Phrase
If someone asks for your 12, 18, or 24 words, private key, keystore file, two-factor authentication code, or remote access to your computer, end the conversation. Block the account and report it through an official channel. Even a partially exposed seed phrase should be considered compromised.
How to Identify a Cloned Account and a Community Inflated with Bots
The age of a channel, its follower count, and a blue check mark do not prove authenticity on their own: an account can be purchased, renamed, or filled with bots. Review its posting history, look for sudden changes in topic, compare views with follower counts, assess the quality of replies, and watch for repetitive comments and identical intervals between reactions.
Disabled comments do not always indicate a scam: they may be turned off because of spam or moderation requirements. The risk increases when questions are also prohibited, criticism is deleted, only profit screenshots are posted, and administrators direct everyone to private messages. A community with tens of thousands of members but almost no meaningful discussion may have an artificially inflated audience.
Why a Promise of Guaranteed Profit Almost Always Indicates a Scam
Guaranteed profit almost always indicates fraud because cryptoasset prices, trading returns, and mining difficulty fluctuate, and losses cannot be ruled out in advance. If the operator promises a fixed return with no risk, conceals the source of the returns, or demands an additional payment before allowing a withdrawal, the figures shown in the dashboard are most likely not backed by real assets.
What Returns Should Raise a Red Flag for Investors
There is no universally safe rate of return: even a modest offer is suspicious if it is described as guaranteed. Offers of 1–3% per day, doubling your deposit in a month, or consistently earning double-digit monthly returns are particularly dangerous. With compounding, 1% per day turns 1,000 units into approximately 3,778 over a year, while 3% turns it into more than 48 million. Such growth is incompatible with a sustainable, legitimate strategy.
An individual token may deliver high actual returns, but this comes with the possibility of an equally large loss. A legitimate service discloses its risks, fees, restrictions, and source of payouts. A fraudulent project shows only its best trades, a countdown to the end of a promotion, and testimonials without verifiable addresses or transaction histories.
How Fake Trading Dashboards and Managed Deposits Work
A fake dashboard displays a balance and profits that exist only in the website’s database. After cryptocurrency is deposited, the operator can fabricate any trade, chart, or return because the user cannot see the assets at an independently verifiable address or confirm that orders were executed. A small initial withdrawal is sometimes processed deliberately to persuade the user to deposit more.
In a managed deposit scheme, an “analyst” promises to trade on the client’s behalf and asks them to transfer funds to the analyst’s address or install a remote-access application. The analyst then shows the account growing and suggests adding more capital. A contract, video call, or photograph of a passport does not make a manager legitimate: the documents may belong to someone else, and the company may be impersonating a real organization.
Why Cloud Mining and Paid Signals May Be Scams
Cloud mining is not inherently fraudulent, but the promised payout should depend on the hashrate, network difficulty, coin price, electricity costs, and operator fees. If a contract guarantees a fixed return regardless of these factors, provides no information about its equipment or mining pool, or sells membership tiers with referral bonuses, payouts may be funded by deposits from new participants.
Trading signals also offer no guarantees. Results are easy to manipulate by deleting an unsuccessful forecast, editing a message, posting opposing recommendations in different groups, or reporting returns without accounting for fees and drawdowns. Verifiable statistics should include every signal over an extended period, the exact publication time, entry and exit rules, maximum drawdown, and results after expenses.
| Offer | How the Appearance of Profit Is Created | Key Risk | Independent Verification |
|---|---|---|---|
| Trading Dashboard | The balance and trades are fabricated within the website | There may be no assets in the account | Verify licensing, custody, and actual withdrawals |
| Managed Deposit | They show reports from a “trader” | The funds are sent to someone else's wallet | Legal entity, authority, custodian, and contract terms |
| Cloud mining | A fixed percentage is credited | The equipment may not exist | Pool, hashrate, payout address, and contract economics |
| Signals | Losses and drawdowns are concealed | The result cannot be replicated | A complete, unedited archive of predictions |
Why you should never pay an additional withdrawal fee or tax
A demand to send more money to unlock a deposit you have already made is one of the clearest signs of a scam. The stated reason may be a tax, insurance, an AML check, a status upgrade, a network fee, or proof of solvency. Once you pay, another charge appears because the displayed balance was never intended to be withdrawn.
Do not try to resolve the issue with one final payment
A legitimate service fee is usually deducted from the available balance, while a network fee is visible on the blockchain and corresponds to a specific transaction. If the platform claims it cannot deduct the payment from your balance, stop, save the addresses, transaction hashes, and correspondence, and contact the exchange through which you sent the funds.
How to safely verify a cryptocurrency offer before sending money
A safe verification process starts with independently finding the original source and analyzing the recipient address and withdrawal terms without following any links you were sent. Do not connect your primary wallet: use a separate empty address, transaction simulation, and a minimal test amount only after completing your checks. Any request to disclose secret information is grounds for immediate refusal.
How to independently verify the source of an offer
Record the project name, exact domain, the other party's username, contract address, and transfer address without interacting with them. Then find the official resource through several independent sources: documentation, a reputable aggregator, a verified developer profile, and a repository. The links should all point to the same domain and contract. A search ad, a message from an administrator, and a QR code from the seller do not count as independent confirmation.
Check the domain registration date, its change history in web archives, and whether its spelling resembles that of a well-known brand. A recently registered domain does not prove fraud, and an old one does not guarantee safety: the domain may have been purchased or compromised. Look for the legal name, country of registration, clear contact details, and regulatory warnings if the service holds funds, accepts deposits, or offers asset management.
How to check a wallet address and smart contract
Enter the address manually into the appropriate network explorer. Make sure the network matches, the contract is verified, and the address appears in the official documentation. Review its age, incoming and outgoing transactions, concentration of funds, interactions with known services, and warning labels. A new empty address may be acceptable for a private seller, but it contradicts a platform's claims of having operated for years.
Do not assume an address is legitimate simply because it holds a large balance: the funds may be stolen, temporarily borrowed, or represented by tokens with no liquidity. For a contract, also check the owner's privileges and whether they can pause transactions, change fees, mint new tokens, block sales, or upgrade the implementation. If you do not understand the code or privileges, failing to find a vulnerability does not mean the contract is safe.
How to check permissions without connecting your primary wallet
Create a separate wallet for verification with a new seed phrase on a trusted device, and do not transfer your main assets to it. Never enter your primary wallet's seed phrase on a new website, import it into a browser extension for testing, or disclose it to a “verifier.” A hardware wallet reduces the risk of key theft but does not protect you if you knowingly sign a malicious permission.
Before confirming, review the network, contract address, amount, transaction type, and allowance limit. An unlimited approve allows the contract to transfer the relevant token in the future; setApprovalForAll applies to an entire NFT collection. Permit can grant permission through a signature without a separate transaction. Use your wallet's simulator or an independent analyzer, but remember that a simulation shows the expected effect and does not guarantee that the project is legitimate.
What information is safe to share for verification
A public address and transaction hash do not grant control over your funds, although they reveal your transaction history and balance. A seed phrase, private key, backup file, password, 2FA code, and one-time confirmation code are secrets. Never share them with support staff, an auditor, or anyone claiming to be an exchange employee.
How to check withdrawal terms and a service's reputation
Before depositing, find the fees, minimum withdrawal amount, list of supported networks, identity verification time frames, limits, reasons for account restrictions, and the account closure procedure. Save a local copy of the terms or take screenshots: a fraudulent website may change the page after you deposit. Do not send money if the withdrawal rules are available only after payment or a manager promises “individual terms.”
Evaluate reviews by their content, not their average star rating. Useful reports include dates, transaction hashes, descriptions of correspondence, and the outcome of the dispute. A large number of similar glowing reviews posted at the same time, along with complaints about being unable to withdraw, matter more than an attractive rating. Also check regulatory warnings, domain blocks, renaming history, and mentions of the addresses in abuse databases.
Can you make a test transfer?
A test transfer is appropriate only after all other checks and does not conclusively prove safety. Send an amount you can afford to lose from a separate wallet, and first try to withdraw it. Account for the minimum withdrawal amount and fees: a scammer may allow a small transaction and then block a large deposit or demand an additional payment.
Do not increase the amount just because the first withdrawal succeeded. Recheck the destination address, network, and rules, set your own risk limit, and do not change it under pressure from a manager. When buying an asset, it is safer to use a reputable platform or a verified smart contract where the transaction is executed atomically than to send coins to a stranger and wait for payment in return.
Safe verification procedure
First verify the source and addresses, then review the contract, permissions, reputation, and withdrawal process. After that, use a separate wallet, run a simulation, and perform a minimum-value test. If even one essential item cannot be independently verified, the right decision is to reject the offer rather than compensate for uncertainty by transferring a smaller amount.
When to immediately refuse a transfer
Refuse if you are being rushed, told not to seek advice, given a different address at the last moment, asked to send funds in multiple transactions, or promised a larger return after a “wallet verification.” The same rule applies if you are asked for secret information or remote access, told to install an unknown app, asked to sign an unclear transaction, or required to pay an additional fee to unlock withdrawals.
Do not let the time already spent or a small initial payment influence your decision. Scammers use escalating commitments: a fee is followed by a tax, then insurance and a penalty. Stopping prevents further losses. Preserve the evidence, revoke dangerous permissions, move the remaining assets if a key has been compromised, and report the sender’s address to the exchange you use.
What you must never disclose or sign in a crypto wallet
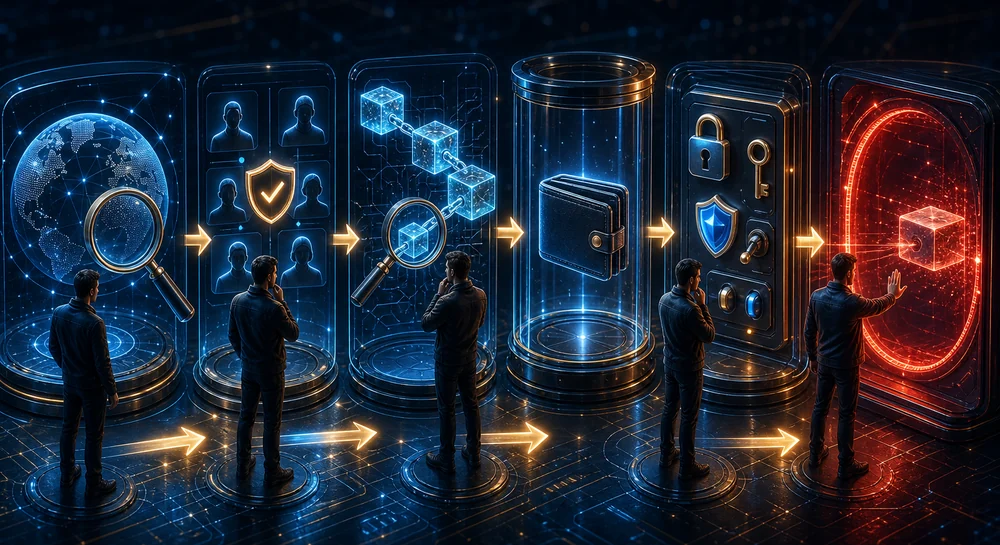
Never disclose your seed phrase or private key, and never approve unclear messages, transactions, or unlimited token spending permissions in your wallet. Even simply connecting to an unknown dApp creates a phishing risk: it does not usually transfer funds by itself, but it sets the user up to provide a dangerous signature.
Why you must never disclose your seed phrase or private key
A seed phrase and private key provide full control over the corresponding addresses. Anyone who obtains them can restore the wallet on another device, transfer coins and tokens, manage NFTs, and continue monitoring incoming funds. Changing the app password, removing the extension, or locking the phone after a leak will no longer protect the assets.
A seed phrase usually consists of 12, 18, or 24 words and is used to restore a set of addresses. A private key corresponds to a specific address. Customer support, community administrators, exchange employees, token developers, and “wallet verification” websites do not need this information. Legitimate support may ask for a public address or transaction hash, but never for secret keys.
If the secret has been exposed, consider the wallet compromised
Deleting the sent message does not resolve the problem. A screenshot or automated bot could have saved the words within seconds. Create a new wallet with a new seed phrase on a clean device and transfer the remaining assets to it. Never use the old phrase again, even after changing the password.
Can you safely sign messages in a wallet?
Signing a message is safe only when the website, purpose of the signature, domain, and displayed text are clear. A signature does not always result in an immediate transfer, but it may confirm a login, acceptance of terms, placement of an order, or an authorization that an attacker can later use to withdraw assets.
Blind signatures are especially dangerous: the wallet may display only a string of characters or warn that it cannot decode the content. Requests to “sign for verification,” “sync your wallet,” “unlock withdrawals,” or “claim compensation” do not explain the legal and technical implications of the action. If the interface does not let you read the request, it is best to reject it.
| Action | What it usually does | Main risk | What to check |
|---|---|---|---|
| Connecting a wallet | Shows the public address to the dApp | A phishing site will prompt you to perform another dangerous action | Domain, network, and list of requested accounts |
| Signing a message | Confirms ownership of an address or intent | The signature may authorize an order or permission | Full text, recipient, expiration, and purpose |
| Confirming a transaction | Records an action on the blockchain | Transfer of funds or a call to a malicious contract | Contract address, amount, network, and simulation |
| Token approval | Allows a contract to spend tokens | The contract may withdraw the approved amount later | Token, spender, limit, and dApp reputation |
Why unlimited token approvals are dangerous
A token approval does not transfer tokens immediately, but grants a spender address the right to use them within the specified limit. Unlimited approvals are often used by legitimate DeFi services for convenience, but if the contract is compromised or the address is replaced, the entire current and future balance of the relevant token is at risk.
It is safer to approve only the amount required for the upcoming transaction and revoke the approval afterward through the wallet interface, a blockchain explorer, or a trusted approval-checking service. Revocation is a separate transaction and requires a network fee. It does not recover funds already withdrawn or revoke approvals on other networks.
A hardware wallet does not prevent careless confirmations: it protects the key from extraction but will execute a transaction that the owner knowingly signs on the device. You should therefore read the device screen as carefully as the browser interface. Keeping a separate “cold” wallet for storage and a spending wallet for dApps significantly limits the potential damage.
What to do if you have already sent cryptocurrency to scammers or connected your wallet
First, stop all contact and make no further payments. Then determine exactly what happened: a transfer, disclosure of a seed phrase, a malicious signature, or an approval. Preserve the evidence, move the remaining assets to a secure wallet, revoke permissions, and notify the exchanges involved. A transaction confirmed on the blockchain usually cannot be reversed.
How to urgently secure your remaining assets
If your seed phrase or private key has been exposed, use a different, trusted device. Create a new wallet with an entirely new recovery phrase and transfer the most valuable and liquid assets first. Then move the remaining tokens and NFTs. You may need the native coin of each network to pay fees, such as ETH, BNB, SOL, or TRX.
Do not import a compromised seed phrase into a new wallet or create a new account under the old phrase: the associated keys will still be accessible to the scammer. If the attacker has installed an automated sweeper that instantly takes any coins deposited to cover fees, attempting to rescue the assets yourself may only increase your losses. In this case, seek help from a trusted specialist without sharing your seed phrase.
If the seed phrase was not exposed and the wallet was only connected to a website, disconnect the session and review approvals on every network you used. Simply disconnecting the dApp in the settings does not revoke permissions recorded on the blockchain. Malicious approvals must be revoked through separate transactions. Also check NFT operator permissions and signatures that allow orders to be executed later.
What to do in the first few minutes
- Close the suspicious website and do not approve any new requests.
- Record the addresses, transaction hashes, domain, correspondence, and time of the incident.
- Create a new wallet on a clean device if the private keys may have been exposed.
- Transfer the remaining assets and revoke approvals on every affected network.
- Change the passwords for linked accounts and enable two-factor authentication.
- Provide exchanges, platforms, and law enforcement with the exact transaction details.
Which passwords and credentials you need to change
Change the passwords for your email, exchanges, cloud storage, and messaging apps if they were used on the infected device or reused across services. Terminate active sessions, remove unknown devices and API keys, and review email forwarding rules. For exchange accounts, enable an authenticator app or hardware security key and set up a withdrawal address allowlist if available.
Scan the device with security software and remove unknown browser extensions and remote-access applications. If there are signs of infection, it is safer to set up a clean system than to continue using the old device. Do not enter a new seed phrase on a computer that may have logged keystrokes, clipboard contents, or screenshots.
What evidence to preserve after a crypto scam
Save the hash of every transaction, the sender and recipient addresses, network, token, amount, date, and time. Take screenshots of the conversation, the scammer’s profile, the advertisement, the website, and the payment page. Export emails with their full headers, record support ticket numbers, and preserve the original files. Screenshots alone are not enough: links, identifiers, and blockchain data make verification easier.
Do not edit the original files or include your seed phrase, private key, backup codes, or personal documents when filing a report. Write a brief timeline: where you saw the offer, how you were contacted, what was promised, what actions you were asked to take, and where the funds went. This helps an exchange or investigator match the addresses and accounts more quickly.
| Situation | First action | What else to check | Can the consequences be reversed? |
|---|---|---|---|
| A standard transfer was sent | Save the hash and notify the receiving platform | Associated addresses and subsequent transfers | The transfer cannot be reversed; the funds may only be frozen by a service |
| Token approval granted | Revoke the permission on the relevant network | Other tokens, NFTs, and networks | Future transfers can be stopped, but past ones cannot |
| Seed phrase exposed | Move the assets to a wallet with a new seed phrase | All addresses and networks associated with the old wallet | The old wallet cannot be made secret again |
| Exchange account hacked | Block withdrawals through support | Email, sessions, API keys, and 2FA | Sometimes a withdrawal can be stopped before it is processed |
Who to contact after sending funds to scammers
If the funds reached a centralized exchange, immediately send its security team the transaction hash, deposit address, amount, time, and official police report number once available. The exchange may be able to restrict the recipient’s account, but it generally will not disclose their details to a private complainant or return assets without a legal basis.
File a report with the police or the cybercrime unit in your country. You should also report the phishing domain to the hosting provider, registrar, search engine, social network, or app store. If the incident involves a particular exchange, wallet, or dApp, use only the contact details on the official website whose address you entered manually.
Beware of crypto recovery scammers
After you publish an address or complaint, “blockchain investigators,” “lawyers,” and “hackers” may approach you, promising guaranteed recovery in exchange for an upfront payment, tax, or unlocking fee. Do not send them money or disclose your keys. Legitimate experts cannot reverse a transaction or guarantee recovery.
The chance of recovery depends on the route taken by the funds. It is higher if the transfer quickly reached a regulated centralized platform and its security team was notified before the funds were withdrawn. It is significantly lower after the funds have passed through a decentralized service, bridge, mixer, or chain of new addresses. Blockchain analysis can help trace their movement, but does not itself provide the legal authority to seize someone else’s coins.
What to do next: common questions about crypto scams
After initially securing your wallet, check your other networks and accounts, preserve the evidence, and submit reports to the platforms used by the scammer. Do not pay to “unlock” a recovery or trust promises of guaranteed tracing. Audits, KYC, and positive reviews only reduce certain risks; they do not prove that a project is safe.
Continue monitoring the compromised addresses through blockchain explorers, but do not send any new funds to them. Warn your contacts if the scammer gained access to your account and may message them in your name. For future transactions, separate storage from dApp interactions: keep your main balance separate and transfer only the amount needed for a specific transaction to a spending address.
No single indicator—such as a well-known investor, completed KYC, a contract audit, a social media badge, or profits earned by early participants—can replace comprehensive due diligence. Security depends on a combination of key control, transaction transparency, limited exposure, and the ability to independently verify every claim.
Frequently asked questions
Can cryptocurrency sent to a scammer be recovered?
A confirmed transaction cannot be reversed like a bank payment. Recovery may be possible if the recipient agrees to return the funds, or if a centralized platform freezes them in time and receives a legal basis for releasing them. The sooner you save the hash and address and submit reports, the better the practical chance of recovery, but there are no guarantees.
Is it safe to complete KYC for a crypto project?
It is safer to complete KYC only with a reputable platform that has a clearly identified legal entity, a data processing policy, and a secure domain. Sending your passport to an unknown project creates a risk of identity theft. Requiring documents does not in itself prove legitimacy, while the absence of KYC does not always indicate a scam.
What does a smart contract audit mean?
An audit means that specialists reviewed a specific version of the code at a particular point in time and documented the risks they found. It does not guarantee that the code is error-free, that the team is honest, that liquidity is sufficient, or that a rug pull is impossible. Verify the auditor, contract address and version, report date, unresolved findings, and administrator privileges.
Can reviews of a crypto project be trusted?
Reviews should be treated as an additional signal, not as proof. Scammers buy comments, create aged accounts, and remove complaints; competitors may also post false negative reviews. It is more useful to look for independent discussions containing verifiable transaction hashes, compare dates, and check for identical wording across different sources.
Where should you report a crypto scam?
Report it to the police or national cybercrime unit, the security team of the exchange involved, the social network’s administrators, and the owner of the platform where the advertisement appeared. You can report a phishing domain to its registrar and hosting provider. Include the network, addresses, hashes, amounts, times, and links in your report.
Does a blocked withdrawal mean you need to pay an additional tax or fee?
No. A demand for another payment to withdraw “profits,” pay a tax or insurance charge, or unlock funds is a typical sign of an ongoing scam. Legitimate fees are generally deducted from the available balance or disclosed in advance in the service’s terms. Do not pay again, and document every demand as evidence.